What Is a Reverse Proxy? A Beginner's Guide with Examples
A reverse proxy is a server that sits in front of your web servers and receives every request from the internet first. It decides which server should handle each request, forwards it, and sends the response back to the visitor, who never talks to your servers directly.
Have you ever wondered how websites handle HTTPS, spread traffic across many servers, or block bad traffic before it reaches the app? Most of the time, a reverse proxy is doing it. In this guide, we'll unpack what a reverse proxy is, how it works, and how to set one up.
In this guide:
- How a reverse proxy works
- Reverse proxy vs forward proxy
- Why use a reverse proxy?
- Reverse proxy vs load balancer vs API gateway
- Popular reverse proxies
- Set up a reverse proxy: nginx and Caddy examples
- Reverse proxies and custom domains
How a reverse proxy works
Think of a reverse proxy as a middleman between users and your servers. Here's what happens step by step:
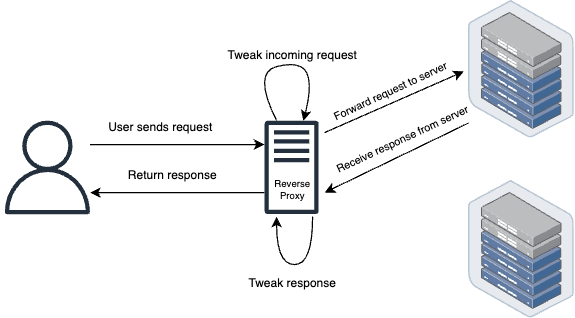
- The user sends a request. Someone visits your website. DNS points your domain at the reverse proxy, so the request goes there instead of straight to your server.
- The proxy adjusts the request. It might remove parts that aren't needed, or add information your server needs, like the visitor's real IP address in an
X-Forwarded-Forheader. - It decides where to send it. If you have more than one server, it picks one, based on the path, the hostname, or which server is least busy.
- Your server responds. The chosen server handles the request and sends the response (like a webpage) back to the proxy.
- The proxy adjusts the response. It can compress it, cache it for the next visitor, or add security headers.
- The visitor gets the response. As far as they can tell, they only ever talked to one server.
The main goal is that everything runs smoothly. The proxy manages traffic so no server gets overloaded, makes sure users get the right data, and improves performance and security along the way.
Reverse proxy vs forward proxy
Both sit in the middle of a connection. The difference is whose side they're on.
Imagine you're at a massive library, where books represent the websites or online resources you want to access.
Forward proxy: you want to borrow a specific book, but you don't want the librarians (websites) to know who's borrowing it. So you ask a friend (the forward proxy) to get it for you. The librarians only see your friend and have no idea you're the actual reader.
Reverse proxy: now imagine the library uses helpers (reverse proxies) to manage the books. Instead of searching the vast storage area yourself, you talk to a helper. The helper knows which shelf (server) has your book and fetches it. They also keep popular books at the front desk (caching) and share the work between several storage rooms (load balancing), so the main storage area doesn't get overwhelmed.
| Forward proxy | Reverse proxy | |
|---|---|---|
| Works for | The client (users) | The server (website owner) |
| Sits in front of | Users' devices | Web servers |
| Hides | Who the user is | Which servers are behind it |
| Typical uses | Company web filters, VPN-style privacy, getting around blocks | HTTPS, load balancing, caching, security |
| Configured by | The user or their IT team | The website's team |
Why use a reverse proxy?
- HTTPS (TLS termination): the proxy holds the certificates and handles encryption, so your app servers don't have to. One place to renew certificates instead of every server.
- Load balancing: when one server isn't enough, the proxy spreads requests across several and stops sending traffic to any that fail health checks.
- Security: your servers' addresses stay hidden, and the proxy can rate-limit, block bad IPs or run a web application firewall before anything reaches your app.
- Caching: the proxy can keep copies of responses and serve repeat requests itself, which takes load off your servers.
- Compression: it can gzip or Brotli-compress responses so pages load faster.
- One entry point for many services:
/apican go to one service and/blogto another, while visitors see a single domain. - Zero-downtime deploys: the proxy can switch traffic to new servers and drain the old ones, so visitors never see an error.
Reverse proxy vs load balancer vs API gateway
These terms overlap, and one piece of software often does all three.
- A load balancer spreads traffic across servers. Most reverse proxies can load balance, but some load balancers (like AWS's Network Load Balancer) work at the TCP level and never look at HTTP requests.
- A reverse proxy works with HTTP. It can route by hostname or path, change headers, cache and terminate TLS. Load balancing is one of its jobs.
- An API gateway is a reverse proxy specialised for APIs: authentication, API keys, per-client rate limits and request transformations.
Popular reverse proxies
| Software | Good for |
|---|---|
| nginx | The classic. Fast, flexible, and everywhere. Certificates need a separate tool like Certbot. |
| Caddy | Automatic HTTPS out of the box, including certificates on demand for new domains. Short config files. |
| HAProxy | High-performance load balancing at the TCP and HTTP level. |
| Traefik | Containers. It discovers services from Docker or Kubernetes automatically. |
| Envoy | Service meshes and large microservice setups. |
| Cloudflare, AWS CloudFront | Managed reverse proxies at the edge, combined with a CDN. |
Set up a reverse proxy: nginx and Caddy examples
Say your app runs on port 3000 and you want example.com to reach it over HTTPS. With nginx, you forward requests and pass along the original host and the visitor's IP:
server {
    listen 443 ssl;
    server_name example.com;

    ssl_certificate     /etc/letsencrypt/live/example.com/fullchain.pem;
    ssl_certificate_key /etc/letsencrypt/live/example.com/privkey.pem;

    location / {
        proxy_pass http://127.0.0.1:3000;
        proxy_set_header Host $host;
        proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header X-Forwarded-Proto $scheme;
    }
}
You get the certificate files separately, for example with Certbot, and renew them on a schedule.
The same thing in Caddy, which gets and renews the certificate by itself and sets the forwarding headers by default:
example.com {
	reverse_proxy 127.0.0.1:3000
}
Either way, tell your app it's behind a proxy, so it reads the visitor's IP and protocol from the X-Forwarded-* headers. Only trust those headers from your own proxy, because anyone can send them.
Reverse proxies and custom domains
Reverse proxies are also how SaaS products let customers use their own domains, like app.customer.com instead of customer.yourapp.com. Each customer points their domain at your proxy, the proxy gets an HTTPS certificate for it, and it forwards the request to your app with the original hostname, so your app knows which customer's content to show.
With a handful of domains, you can list them in a config file. With thousands, you need a proxy that issues certificates on demand, checks with your app before it does, and shares certificates across servers. Our guide to custom domains for SaaS covers how that works, and we have walkthroughs for Rails, Django and Node.js.
That's also what we run: SaaS Custom Domains is a managed reverse proxy for custom domains, so you don't have to operate one yourself.
Frequently asked questions
What is a reverse proxy in simple terms?
A server that stands in front of your website's servers. Visitors talk to it, and it passes their requests to the right server and the responses back to them.
Is a load balancer a reverse proxy?
Often, but not always. An HTTP load balancer is a kind of reverse proxy. A TCP-level load balancer only forwards connections and doesn't look at the requests, so it isn't one in the usual sense.
Is Cloudflare a reverse proxy?
Yes. When a DNS record is "proxied" (the orange cloud), visitors connect to Cloudflare, which forwards their requests to your server.
Is nginx a reverse proxy?
nginx is a web server that's widely used as a reverse proxy, with the proxy_pass directive. Caddy, HAProxy, Traefik and Envoy are common alternatives.
Does a reverse proxy make my site faster?
It can, through caching, compression and keeping connections to your servers open. It also adds one more hop, so a proxy that does none of those things makes requests slightly slower.
Final thoughts
Setting up a basic reverse proxy takes a few lines of config. Mastering the details takes practice: certificates, headers, health checks and caching rules. As you go deeper into web infrastructure, you'll find reverse proxies everywhere, keeping online services fast, secure and available.